CYBERSECURITY
Score and monitor the cybersecurity of your suppliers
Understand the cyber maturity of every supplier and their subprocessors — from governance and access management to incidents and certificates — in one due diligence platform.
Cybersecurity
Overall performance
Weighted average across 19 parameters
Scorecard weight
Scorecard weight in overall supplier score
Artificial intelligence usage and security
Organisational
2x
Asset & information management
Organisational
1x
Cyber insurance
Organisational
1x
Cybersecurity governance
Organisational
2x
Cybersecurity incident management
Organisational
2x
Cybersecurity risk management
Organisational
1x
Information retention and disposal
Organisational
1x
Supply chain security
Organisational
3x
Cryptography and encryption
Technological
1x
Data privacy and protection
Technological
2x
Endpoint protection
Technological
1x
Identity and access management
Technological
4x
Network security
Technological
1x
Secure development
Technological
2x
Security monitoring
Technological
2x
Vulnerability management
Technological
3x
Cybersecurity awareness and training
People
1x
Personnel security
People
1x
Physical security
Physical
1x
CYBERSECURITY ASSESSMENT
Score every supplier on 19 cybersecurity parameters, weighted your way
Parameters are grouped into organisational, technological, people, and physical controls, and anchored to ISO 27001:2022 and NIS2. Each one is assessed from inherent risk, incidents, certificates, documents, and supplier engagement. Customize which parameters apply and how much each one counts.
Cybersecurity (19 parameters)
CYBERSECURITY DUE DILIGENCE
Five steps from supplier name to a complete picture of their cyber maturity
INHERENT RISK
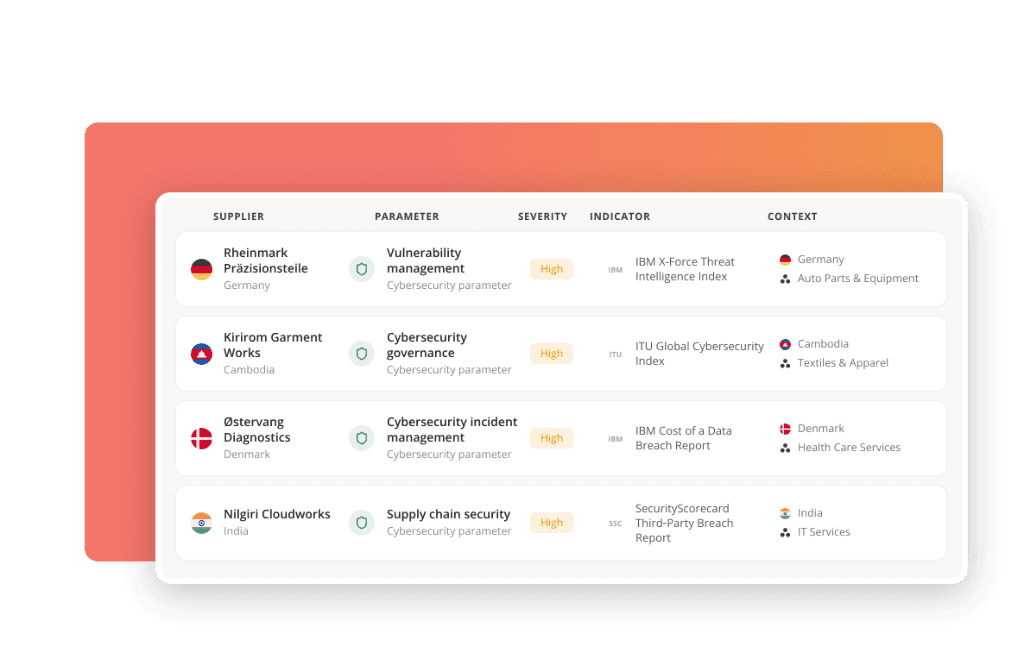
Cybersecurity is no longer just a software vendor question
48% of breaches now involve a third party, up 60% on the year before, rising to 61% in manufacturing and 68% in retail. Cyber risk runs through your full supply chain, not just your software vendors. Responsibly links each supplier's countries and industry to established risk indices for every cybersecurity parameter, so you know which topics are risky with which suppliers before you send a single questionnaire.
SUBPROCESSOR IDENTIFICATION
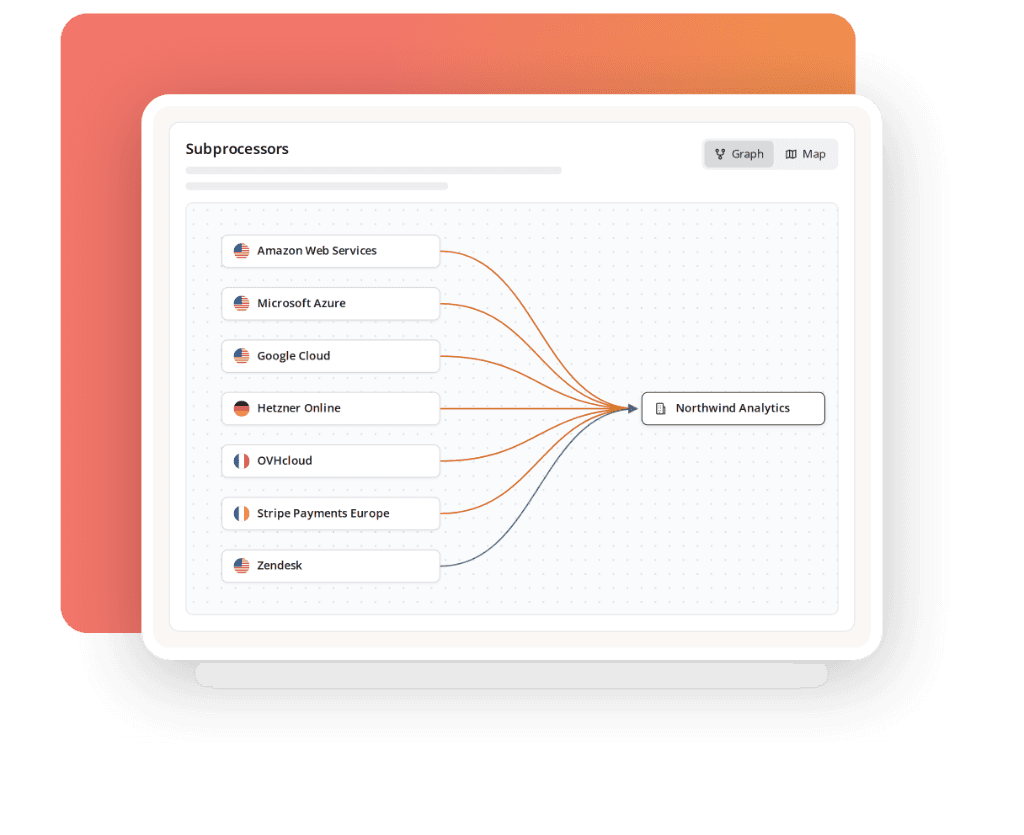
See who your suppliers rely on, without asking
Responsibly automatically maps the subprocessors and material suppliers of your vendors from the subprocessor page on their website, or collects them through engagement. Every subprocessor is tracked for incidents, so you know what may affect your supplier before they notify you.
INCIDENT MONITORING
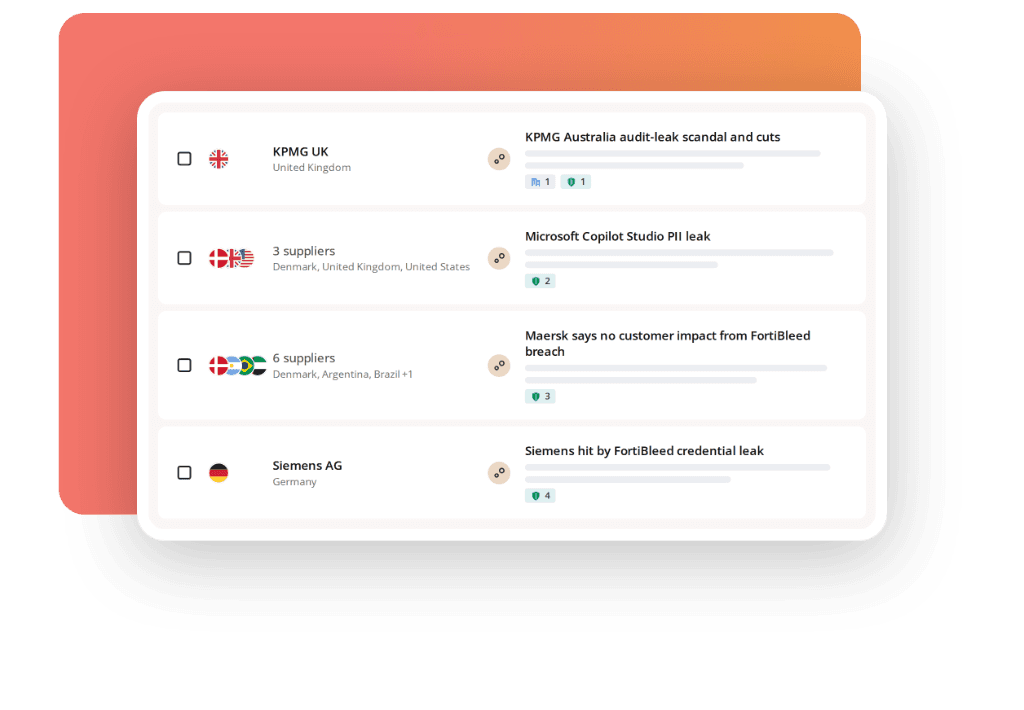
Know about breaches before the notification email arrives
Monitor your suppliers and their subprocessors for breaches, ransomware, and outages across global news. Log incidents your suppliers communicate by email in the same place, and understand each supplier's historical exposure to incidents.
CERTIFICATES, AI ANSWERS AND AUDITS
Understand the maturity of supplier practices in seconds
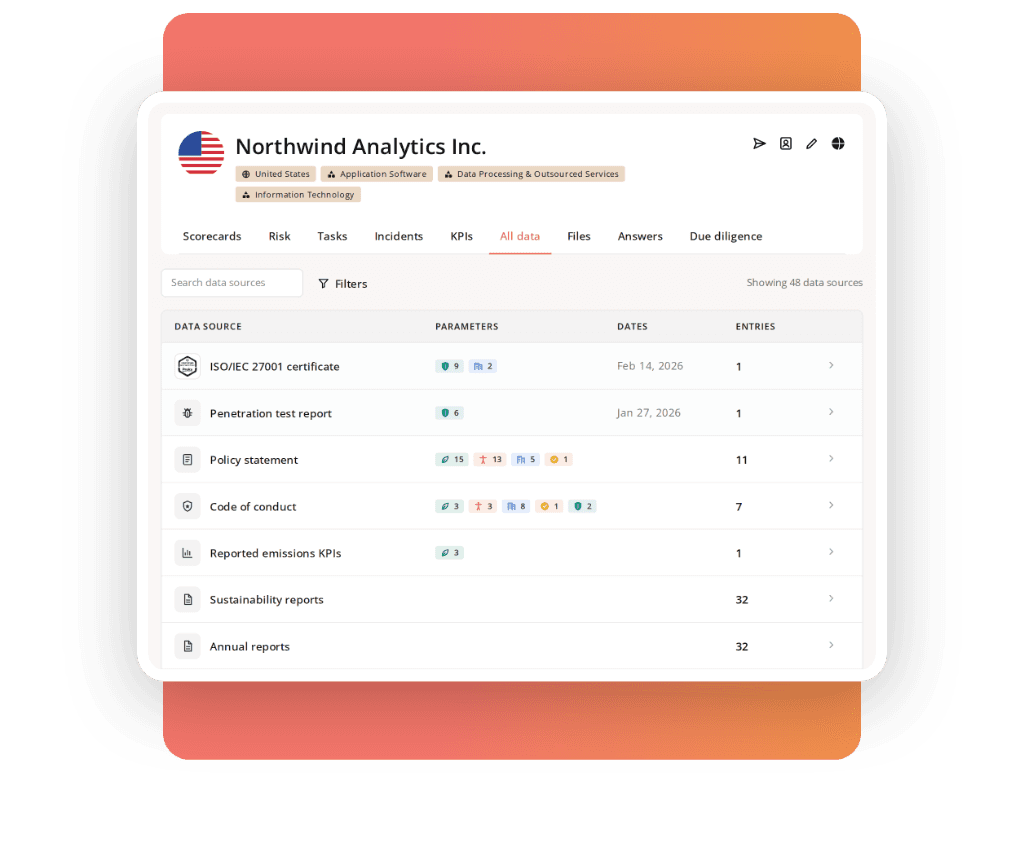
Responsibly automatically picks up and validates certificates such as ISO 27001 and SOC 2, matched to the right legal entity and checked for expiry. Store audit and pentest results in one place, and query the supplier's digital twin for an immediate overview of the maturity of their practices.
SUPPLIER ENGAGEMENT
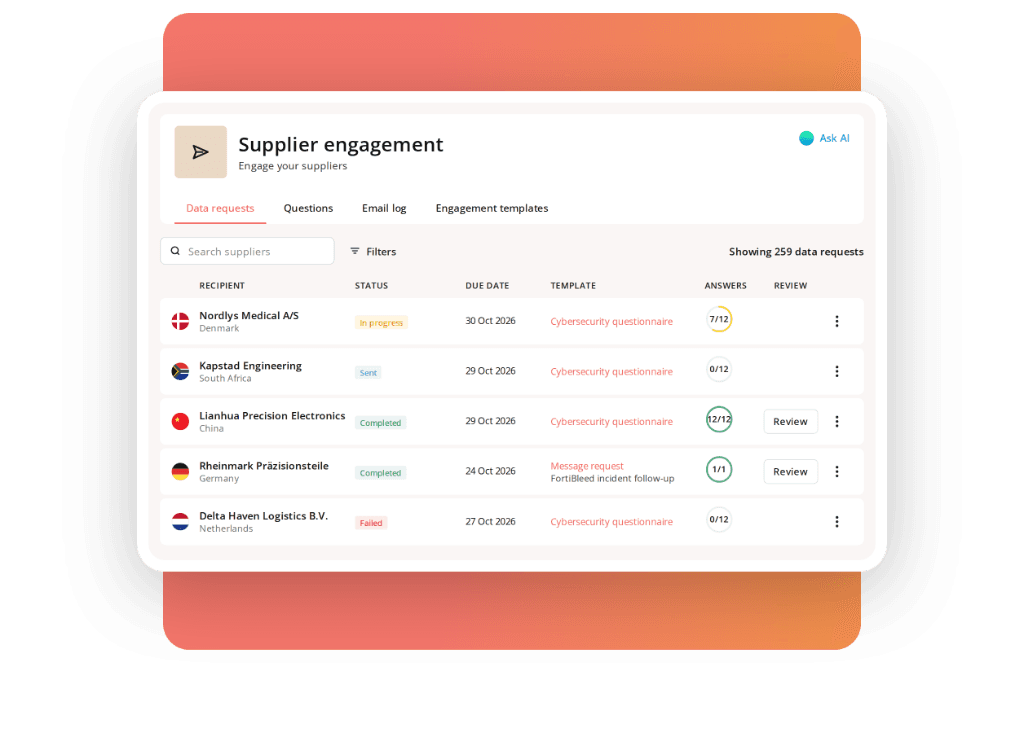
Security questionnaires that adapt to each supplier
Automate engagement of your suppliers. Large cybersecurity questionnaires become dynamic, adapting to each supplier's risk profile and certifications so they only answer what you don't already know. Send-out, scoring, and review happen in one place.
COMPLIANCE
Meet vendor due diligence requirements with evidence to show for it
NIS2, ISO 27001 and SOC 2 all ask the same of you: assess the cyber risk your suppliers bring, keep watching it, and be able to prove it.
- Risk-based supplier assessment
- Continuous monitoring of suppliers and their sub-processors
- Review of supplier incidents
- Audit-ready evidence trail
EU regulation
- Vendor analysis
- Take into account each direct supplier’s vulnerabilities and the quality of its cybersecurity practices, including secure development.
- Vendor monitoring
- Monitor changes in suppliers’ security practices and review incidents involving their products and services.
- Vendor engagement
- Set security requirements in supplier contracts (incident notification, audit rights, rules for subcontractors) and keep a supplier register.
Art. 21(2)(d) and 21(3); Implementing Regulation (EU) 2024/2690, Annex §5
EU regulation · financial entities
- Vendor analysis
- Run due diligence on ICT providers before contracting, including the subcontractors behind critical or important functions.
- Vendor monitoring
- Keep a register of all ICT third-party arrangements and track changes in each provider’s subcontracting chain.
- Vendor engagement
- Contracts must cover security, incident support, audit and access rights, and exit strategies.
Art. 28 and 30; Delegated Regulation (EU) 2025/532
EU regulation · product manufacturers
- Vendor analysis
- Exercise due diligence when integrating third-party components, including open source, so they don’t compromise product security.
- Vendor monitoring
- Track vulnerabilities in integrated components through the support period. Reporting of actively exploited vulnerabilities applies from 11 September 2026.
- Vendor engagement
- Document components in a software bill of materials and report vulnerabilities found in components to their maintainers.
Art. 13(5)–(6), Art. 14, Annex I Part II; full application 11 December 2027
EU regulation · all controllers
- Vendor analysis
- Use only processors that give sufficient guarantees of appropriate technical and organisational security measures.
- Vendor monitoring
- Processors must demonstrate compliance and allow audits; you must be told of sub-processor changes and be able to object.
- Vendor engagement
- Sign a data processing agreement with mandatory terms, flowed down to every sub-processor.
Art. 28 and 32
Certification standard
- Vendor analysis
- Evaluate and select suppliers according to the information security risk they pose.
- Vendor monitoring
- Regularly monitor, review and evaluate supplier security and service delivery, and reassess when services change.
- Vendor engagement
- Agree security requirements in supplier agreements and flow them down the ICT supply chain to sub-suppliers.
Clause 8.1; Annex A 5.19–5.23
AICPA attestation
- Vendor analysis
- Assess and manage risks from vendors and business partners. Criterion CC9.2 is part of every SOC 2 report.
- Vendor monitoring
- Assess vendor performance, act on issues found, and monitor subservice organisations, typically by reviewing their SOC reports.
- Vendor engagement
- Set requirements for vendor engagements and obtain confidentiality and privacy commitments.
Trust Services Criteria CC9.2
AI management system certification
- Vendor analysis
- Ensure AI services, products and materials from suppliers align with your approach to responsible AI.
- Vendor monitoring
- Implementation guidance calls for ongoing evaluation of suppliers’ AI practices as tools, models and data flows change.
- Vendor engagement
- Allocate responsibilities between you, your suppliers and partners across the AI system lifecycle.
Annex A.10.2–A.10.3
Automotive · VDA ISA
- Vendor analysis
- Subject contractors and cooperation partners to an information security risk assessment.
- Vendor monitoring
- Verify that contractors comply with agreed requirements and review their service reports.
- Vendor engagement
- Secure requirements by contract, pass customer requirements on, and flow them down to subcontractors.
VDA ISA 6.1.1–6.1.2
Voluntary framework · US and global
- Vendor analysis
- Identify suppliers, rank them by criticality and perform due diligence before entering a relationship.
- Vendor monitoring
- Assess, record and monitor supplier risk for the full length of the relationship.
- Vendor engagement
- Build security requirements into contracts and include suppliers in incident planning, response and recovery.
GV.SC-04 to GV.SC-08